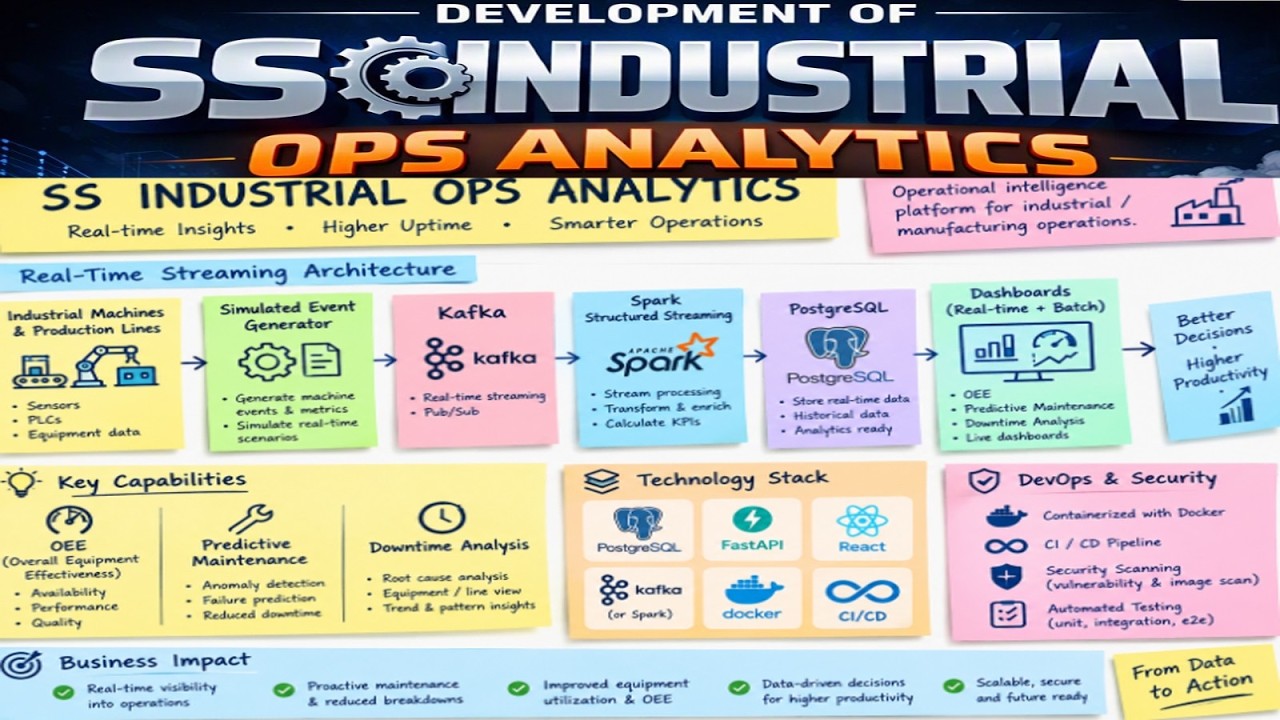
🎯 The vision is simple: connect industrial data, analytics and AI to help teams understand performance, downtime, quality, machine health and production bottlenecks in one operational intelligence platform.
This is the beginning of a demo series covering the complete journey — from data generation and analytics to automated testing, streaming and CI/CD.
⭐
Follow the Complete Engineering Journey
Subscribe for more full-stack development, automated testing, CI/CD, DevOps, quality engineering, security, and software engineering projects.
Containers provide an efficient way to isolate applications,
but their isolation depends heavily on the security of the
underlying container runtime and host operating system.
Container security is therefore not limited to application
images. The runtime, Linux kernel, host configuration,
privileges, permissions, and monitoring controls all
contribute to the overall security boundary.
🔐 Key Security Principle
A container boundary should be treated as a security
boundary that must be continuously protected, monitored,
patched, and properly configured.
Container → Runtime → Host
The relationship between these three layers is central
to understanding container security.
📦
Container
Application workload and isolated process environment.
⚙️
Runtime
Component responsible for creating and managing
containers.
🖥️
Host
Operating system and infrastructure supporting
container workloads.
Why Container Runtime Security Matters
Container security is not limited to application images.
A secure environment also depends on several layers of
infrastructure security.
✓
Container runtime security
✓
Linux kernel security
✓
Host operating-system configuration
✓
Container privileges and capabilities
✓
Runtime permissions
✓
Security controls and monitoring
✓
Timely vulnerability management
01
Container
02
Runtime
03
Kernel
04
Host
Security Impact
If isolation controls are weakened, the impact of a
container compromise can potentially extend beyond the
individual application workload.
Container isolation is not an absolute security boundary.
Vulnerabilities or misconfigurations involving container
runtimes and privileged components can potentially turn
a container compromise into a host compromise.
Security Recommendations
✓
Keep Docker and the container runtime updated.
✓
Apply security patches promptly.
✓
Minimize container privileges.
✓
Follow container-hardening best practices.
✓
Monitor runtime and host activity for suspicious behaviour.
✓
Regularly assess container environments for security weaknesses.
✓
Review exposed capabilities and unnecessary permissions.
🛡️ Key Takeaway
A compromised container should not automatically become
a compromised host. However, weaknesses in the container
runtime, host configuration, or privileged components can
make that boundary vulnerable.
Security Engineering Playlist
Explore the complete security engineering series,
demonstrations, testing workflows, and related topics.
💡 What happens when a professional-looking website combines fake rewards, countdown timers, testimonials, and alarming security warnings?
This educational cybersecurity demonstration explores how a seemingly harmless webpage can be engineered to create urgency, trust, and fear — the exact psychological levers frequently abused in real-world malicious campaigns.
🔴 The Attack Chain STEP-BY-STEP
🎣 The Hook — Social Engineering Triggers
Fake rewards, countdown timers, testimonials, and alarming warnings work together to rush your judgment before your skepticism wakes up. Urgency, trust, and fear — the classic trifecta.
The demo presents a simulated local-file-access scenario to illustrate why browser security boundaries and isolation mechanisms are critical — and what's at stake when they're challenged.
💥 Potential System Impact
In a real-world vulnerability scenario, a compromised browser could become a pathway toward serious system compromise. The exact impact depends on the vulnerability, browser protections, operating system, permissions, and whether additional security controls are bypassed.
🧠 The Biggest Lesson
🚫 Don't judge a website by how professional it looks.
A polished interface does NOT automatically mean a website is trustworthy.
🛡️ Your Defensive Playbook CHECKLIST
✅Keep browsers & operating systems fully updated
✅Use trusted and verified websites only
✅Review browser permissions carefully
✅Avoid suspicious downloads & unexpected prompts
✅Distrust "too good to be true" offers
✅Never let urgency or fear override security judgment
✅Treat unexpected security warnings with skepticism
🔐 SECURITY AWARENESS MATTERS
This project was created purely for educational and security-awareness purposes.
The objective is to demonstrate how malicious-looking webpages use social engineering, deception, urgency, and simulated technical compromise to influence users — and why understanding these techniques is a core cybersecurity skill.
spot the tricks → stop the attack
click without thinking
trust without verifying
proceed without securing
think before you click
verify before you trust
secure before you proceed
📡 Follow the Complete Engineering Journey
Subscribe for more security, full-stack development, automated testing, CI/CD, DevOps, quality engineering, and software engineering projects.
📁 What this demo covers: An Oracle database security assessment using an automated
scanning tool that examines database services, network exposure, patch coverage,
authentication controls, privileges, and potential attack paths — all within
a structured security assessment workflow.
🧮 Key Security Lessons
🔒A latest-version database can still have security findings.
🔒Database security requires more than version management.
🔒Credential, privilege, OJVM, TNS, XDB, and ORDS services should be continuously monitored.
🔒Patch coverage should be measured by service, severity, and exposure.
🔒Exposed listeners should be continuously monitored.
🔒Manual review is also important for validating automated scan results.
🔒Remediation should be prioritized by business risk and exploitability.
🎯 Final Takeaway
This demonstration shows how an automated Oracle database security scanner can combine
network discovery, service detection, database assessment, patch analysis,
credential testing, privilege review, and exploitation-oriented checks
into a single security report.
⚠️ Security Takeaway
🟢Keeping a database up to date is important — but continuous assessment is equally essential.
🔵Scan regularly.Patch quickly.Reduce exposure.Protect the data.
SCAN • PATCH • HARDEN • REPEAT
📺 Complete Video Playlist
Oracle Security Series
📚 all episodes in one place — bookmark for later
🌟
Follow the Complete Engineering Journey
Subscribe for more security, full-stack development, automated testing,
CI/CD, DevOps, quality engineering, and software engineering projects.
From SQL Discovery & Reconnaissance to Critical Security Findings
🛡️ What happens when Microsoft SQL Server goes through a
security-focused assessment?
This demo walks through a complete security assessment of a
SQL Server Express instance — SQLEXPRESS,
covering discovery, reconnaissance, security probes, database auditing,
risk analysis, and final security findings.
⚠️ The key lesson is simple:
being patched does not automatically mean being secure.
🔎 01 — SQL Discovery | Know Your Target
🧭 02 — Reconnaissance | Understand the Environment
🧪 03 — Security Probe | Test the Controls
🚨 OVERALL RISK RATING
CRITICAL
Target: SQLEXPRESS
🔴2
Critical
🟠3
High
🟡3
Medium
🔵4
Low
⚪2
Info
🟢24
Passed
🎯 Final Security Takeaway
A SQL Server can be fully patched and still present significant
security risk.